Hoxhunt trains employees. Noon stops the attack too.
Noon combines adaptive simulations and training with direct email and device protection.


Why teams switch from Hoxhunt to Noon
Only analyzes emails employees report.
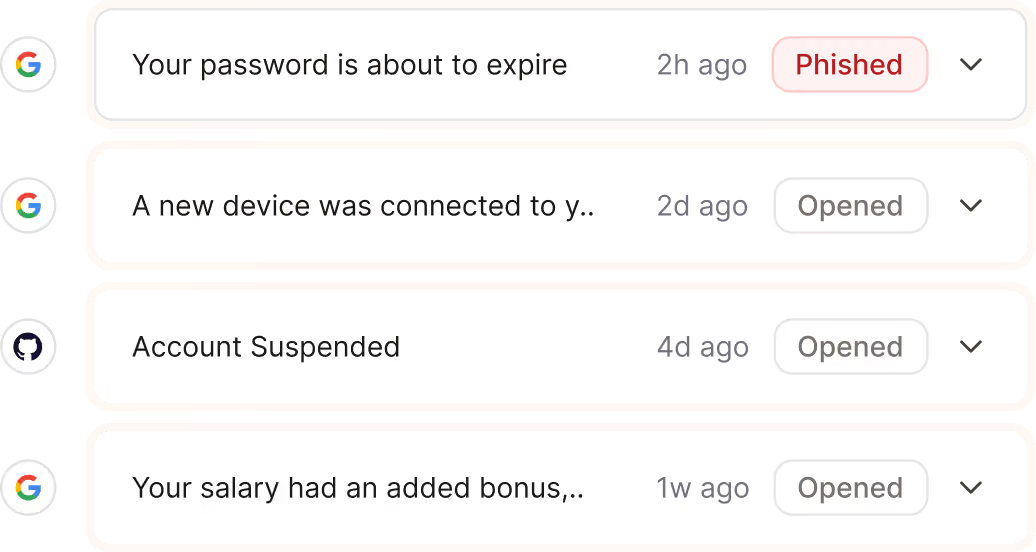
Noon scans every inbound email and flags phishing, BEC and impersonation before anyone clicks, including the ones nobody reports.
Trains for the click, does not protect after it.
Noon keeps protecting after the click: it stops malware before it runs and blocks malicious extensions and risky sites on the laptop.
Needs another tool to see how employees use AI.
Noon shows which AI tools each employee uses, lets teams set policies by app and keeps sensitive data out of AI prompts.
Noon vs Hoxhunt at a glance
“The first simulation-based security training that does it right. Our company gets actual value.”
CTO of European Neo Bank
Train, protect and respond in one platform
Every inbound email checked
Noon connects to Microsoft 365 or Google Workspace by API. It catches phishing, BEC and impersonation, warns on borderline emails, and removes confirmed threats across inboxes.
Executive, vendor and colleague impersonation, even from clean domains
Warning banners for suspicious but legitimate-looking email
One-click reporting with automatic triage
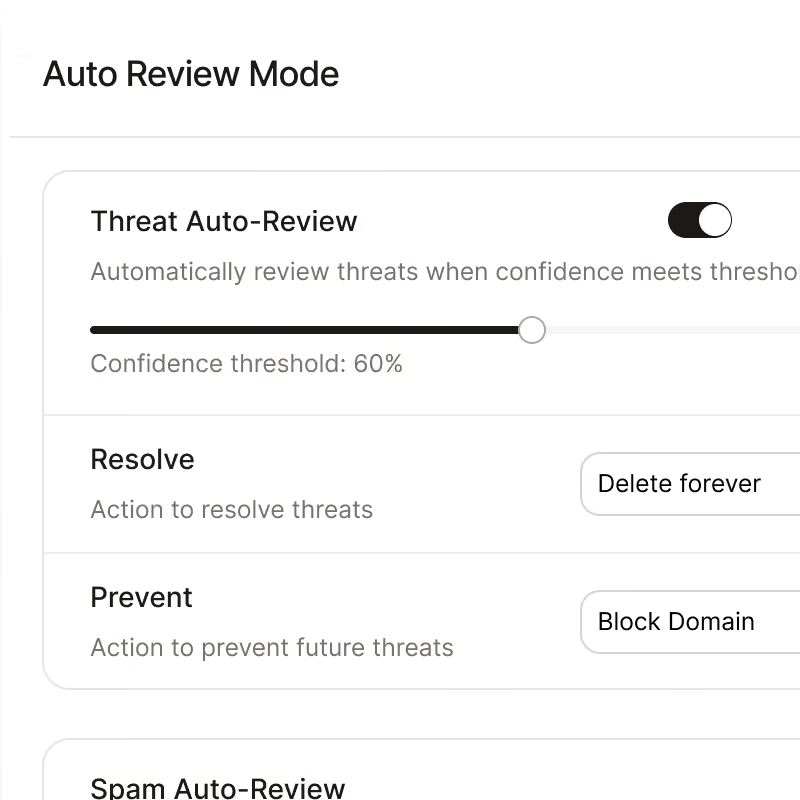
Simulations built on real-world attacks
Scenarios come from real-world attacks and adapt to each employee by role and risk. Campaigns run automatically, with immediate follow-up when someone clicks.
Lookalike domains, deepfake voice, SMS, chat, QR and multi-step attacks
AI scenario builder from a simple attack description
Automated campaigns with risk-based targeting
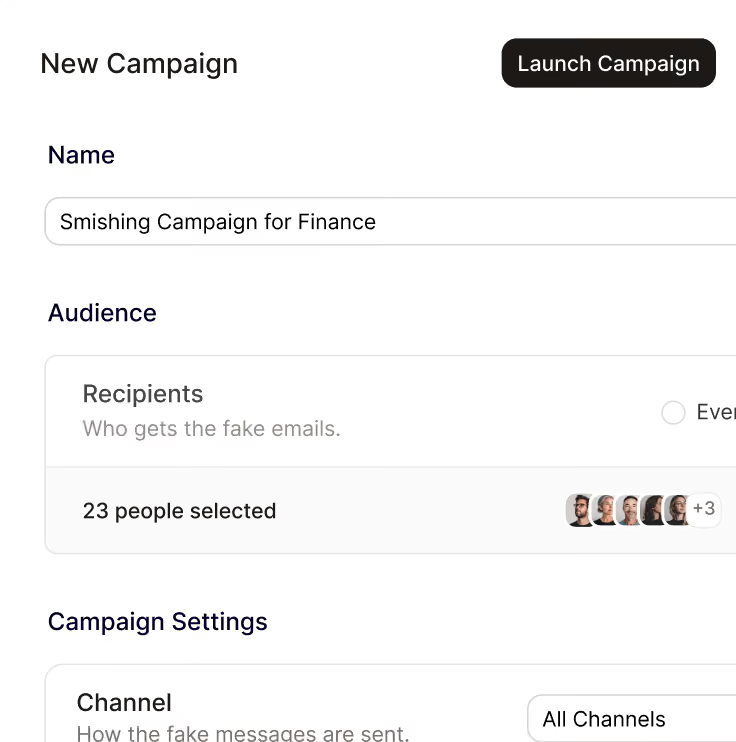
Short interactive training in Slack or Teams, not PDFs and decks
Short interactive lessons arrive in Slack, Teams, Google Chat or email, triggered by employee behaviour and tailored to the risks of each role.
Role-based training for finance, HR, engineering and leadership
Compliance training with completion tracking
AI builder turns policies and incidents into training
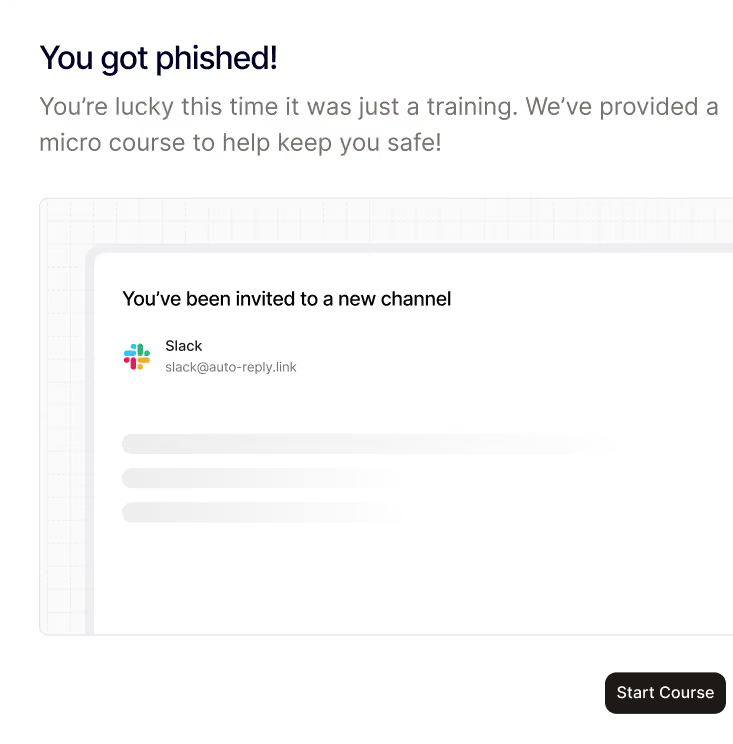
Protection after the click
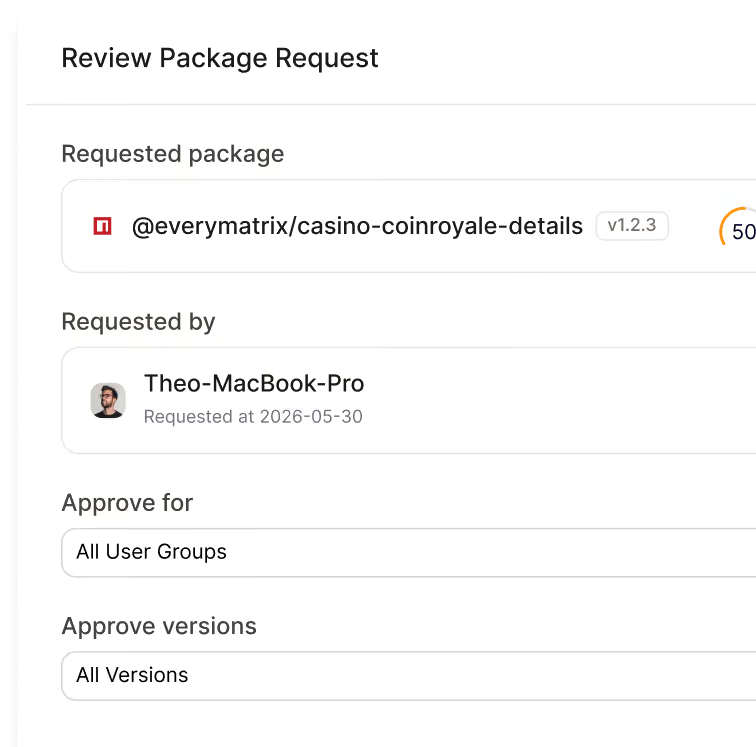
When someone clicks anyway, Noon keeps protecting on the device: blocking phishing sites, malicious downloads and rogue browser extensions, while finding exposed secrets.
Malware from phishing blocked on the device
Malicious extensions and risky sites blocked by policy
API keys and passwords in plain text detected
Your workforce, secured by noon
Be first to protect your people and their devices with Noon.
Frequently Asked Questions
Questions about getting started with Noon Security, phishing, Shadow AI or general employee security
How does Noon compare with Hoxhunt for phishing training?
How does Noon compare with Hoxhunt for phishing training?
Hoxhunt focuses on simulations, training and emails employees report. Noon does that too, but also scans every inbound email automatically and protects the device in the same platform.
Can Noon replace Hoxhunt for simulations and training?
Can Noon replace Hoxhunt for simulations and training?
Yes. Noon covers personalised phishing simulations, role-based training and compliance training.
How long does rollout take?
How long does rollout take?
Hoxhunt uses custom pricing and a guided implementation process. Noon connects, scans and launches your first campaign in a couple of minutes.
Does Noon protect real email too?
Does Noon protect real email too?
Yes. Noon checks inbound email directly, catches phishing, BEC and impersonation, warns on borderline emails and removes confirmed threats across inboxes.
Can Noon run alongside Hoxhunt while we switch?
Can Noon run alongside Hoxhunt while we switch?
Yes. Noon can be added without replacing your existing awareness setup, so you can evaluate email and device protection before moving training and simulations over.